

CargoWise WebTracker — The Keys Were in the Cargo ↗
Credentials recoverable from a logistics platform's own tracking interface.
On marketing claims nobody checks, the 1,000 projects Anthropic never listed, and why an industry full of experts followed along.
Credentials recoverable from a logistics platform's own tracking interface.
Unauthenticated SQL injection reachable in Drupal core.
Reading arbitrary files pre-authentication, as root, on cPanel.
Tooling for reverse engineering without waiting on vendor firmware.
A reproducible lab for Jolokia XSS, JNDI remote code execution, and recovering credentials from Java heap dumps.
An XSS payload stored as a Google Cloud project name executed months later in the unfiltered project-deletion error message, earning a $5,000 VRP reward, plus the impact argument that got it past a self-XSS classification.
Bug bounty platforms never humanized researchers or triage. Now they're drowning in AI slop and wondering why their best people are leaving.
A start-to-finish walkthrough of using h1-brain on an actual program. From hack() briefing to attack plan.
h1-brain is an MCP server that gives Claude your HackerOne bounty history and a database of public disclosures. Setup and first sync.
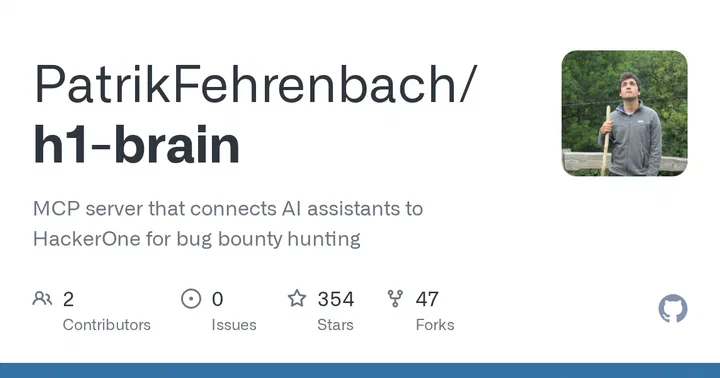
Research tooling
An MCP server that turns your HackerOne report history and public disclosures into a starting point for your next bug bounty hunt.
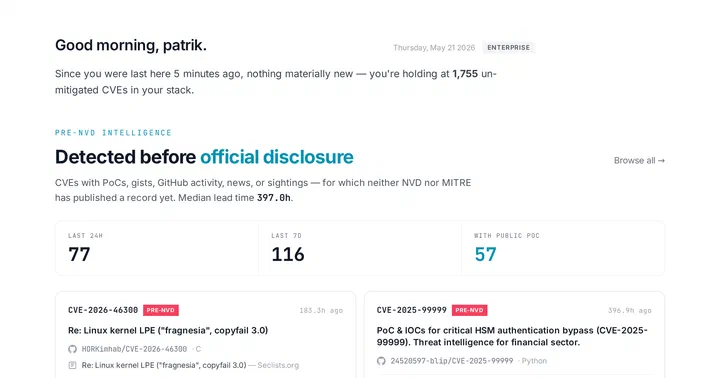
Vulnerability intelligence
A platform that brings together vulnerability disclosures, exploit activity, and threat context to help teams decide what to investigate first.
Security consulting
My security consulting practice, covering penetration testing, security advisory, bug bounty programmes, and vulnerability triage.


